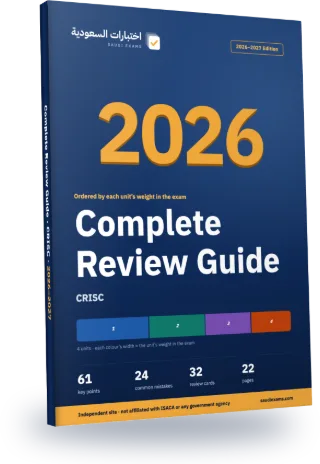
CRISC Complete Review Guide 2026–2027
Every exam topic in a 22-page Arabic PDF, ordered from the heaviest unit to the lightest. The first three chapters alone cover about 80% of the exam questions.
- 22Pages
- 61Key points
- 24Common mistakes
- 32Flashcards
Guide map
Each chapter is one exam unit, ordered by its weight in the real exam.
| Chapter | Unit | Weight | Exam questions | Key points |
|---|---|---|---|---|
| 1 | Risk Response and Reporting | 32% | 48 | 16 |
| 2 | Governance | 26% | 39 | 15 |
| 3 | Risk Assessment | 22% | 33 | 15 |
| 4 | Technology and Security | 20% | 30 | 15 |
Chapter 1 in full: Risk Response and Reporting
32% of the exam, about 48 questions. These are its key points, as in the guide.
- Response selection weighs risk level, cost, benefit, appetite and feasibility; the aim is residual risk within appetite.
- Transferring risk (insurance, outsourcing, contracts) shifts financial impact but not accountability or reputational effect.
- Risk acceptance is a documented decision by an authorized risk owner, with a review date.
The rest of chapter 1, on this page
- Vendor and supply-chain risk: assess before contracting, set security and audit rights in the contract, and monitor performance and incidents.
- Issues, findings and exceptions are tracked with owners and due dates; exceptions are time-bound and approved.
- Control frameworks include COBIT, ISO 27001/27002, NIST SP 800-53 and CIS Controls; choose one that suits the business and regulations.
- Preventive controls stop events, detective controls find them, corrective controls fix them, deterrent controls discourage, compensating controls offset a weaker control.
- Control design starts from the risk and objective; select controls by effectiveness, cost, impact on operations and ease of use.
- Defense in depth and segregation of duties reduce single points of failure.
- Control testing confirms design and operating effectiveness; use walkthroughs, inspection, reperformance and automated testing.
- A risk action plan lists the action, owner, cost, due date and expected residual risk; progress is tracked to closure.
- Key risk indicators are forward-looking metrics that signal changing risk; thresholds trigger escalation.
- Key control indicators measure whether controls are operating effectively; key performance indicators measure how well processes meet goals.
- Aggregate and validate risk data from multiple sources; data quality problems lead to wrong decisions.
- Report in the language of the audience: executives want risk against appetite and business impact; technical teams want actionable detail.
- Emerging risks such as new technology or regulation are scanned continuously and added to the register early.
Common mistakes in this chapter
- The risk practitioner does not accept risk for the business.
- A KRI is not a KPI; KRIs forecast risk.
- Transfer does not remove accountability.
- An exception without an expiry date becomes a permanent weakness.
- Selecting the strongest control regardless of cost is wrong.
- A control that is well designed may still fail operationally.
The other chapters are in the full guide
One purchase · lifetime access · review guide included
7-day review plan
The chapters are spread over 6 days by weight so each day carries a similar load. Day 7 is a full exam.
Day 1 · 32% of the exam
Chapter 1: Risk Response and Reporting
Day 2 · 26% of the exam
Chapter 2: Governance
Day 3 · 22% of the exam
Chapter 3: Risk Assessment
Day 4 · 20% of the exam
Chapter 4: Technology and Security
Day 5
Full mock exam: 150 questions in 240 minutes, then review the common mistakes in the units where you lost marks.
Before you read: see your score today
10 free questions from the main units, no sign-up. Then you know which chapter to start with.
Try 10 free questions and see your levelA look at each chapter
The first three key points of each chapter, as they appear in the guide (in Arabic in the PDF).
Chapter 1: Risk Response and Reporting
- Response selection weighs risk level, cost, benefit, appetite and feasibility; the aim is residual…
- Transferring risk (insurance, outsourcing, contracts) shifts financial impact but not accountability or reputational effect.
- Risk acceptance is a documented decision by an authorized risk owner, with a review…
Chapter 2: Governance
- IT risk is the business risk associated with the use, ownership, operation, involvement, influence…
- The board and executives are accountable for risk; risk governance defines who decides, who…
- Three lines
Chapter 3: Risk Assessment
- A risk event is something that, if it happens, affects objectives; identify events through…
- A risk scenario describes a threat actor or event, the asset affected, the vulnerability…
- Threat modeling identifies how an attacker could target a system, such as with STRIDE;…
Chapter 4: Technology and Security
- Confidentiality prevents unauthorized disclosure; integrity prevents unauthorized change; availability ensures timely access.
- Enterprise architecture documents business, data, application and technology layers; a roadmap shows planned change…
- Technology operations management covers incident, problem, change, configuration and capacity management.
The full guide comes with lifetime access
The full guide (22 pages) is included with lifetime access to this exam, together with every question and full mock exam. Chapter 1 is free for everyone.
Questions about the guide
Is the guide free?
Chapter 1 is free to read on the guide page. The full guide comes with lifetime access to this exam; 7-day access does not include it.
Is it up to date for 2026–2027?
Yes. Unit weights and exam facts follow what the exam body last published, and the last check date is printed in the guide. If the standards change we update the file and buyers download the new version.
Does the guide have questions?
No. The guide covers key points and common mistakes; scoring, weak-area practice and full mock exams are on the site.
Can I read it on my phone?
Yes. A5 pages in a single column, with chapters linked from the contents.
- Pages
- 22
- Edition
- 1448 AH · 2026–2027
- Language
- Arabic
- Last updated
All Engineering Exams review guides
Back to CRISC – Certified in Risk and Information Systems Control (ISACA)
Buy this exam
Pick the access that lasts until your test date.
Included
- Full mock exams: 150 questions in 240 minutes, with a score for every unit
- 750 questions, every option explained with its source
- Practice that starts with your weakest units, plus a review of your mistakes
- Complete Review Guide 2026–2027 (PDF), with lifetime access only
Continue with your Google account and you go straight to the payment page.
You pay on the Waffo Pancake checkout page (in English). The amount is in US dollars and your bank converts it to riyals. One payment with no automatic renewal, by Visa, Mastercard (a mada card with either logo works too), Apple Pay or Google Pay. Your statement shows "WAFFO". Purchases are not refundable.